Information security policy template for UK accountancy practices
The IT security policy, disaster recovery plan, staff acknowledgement and asset register a small practice needs, with the technical rules taken from the Cyber Essentials requirements.
UK practicesGlobal library · 101 packs
Get this pack and 100 more for $129
IT security · this packAML complianceCharity accountsEstate administrationMTD for Income TaxP11D and payrollingUK SRS readinessCarbon reduction planCIS+ 92 more
What's inside
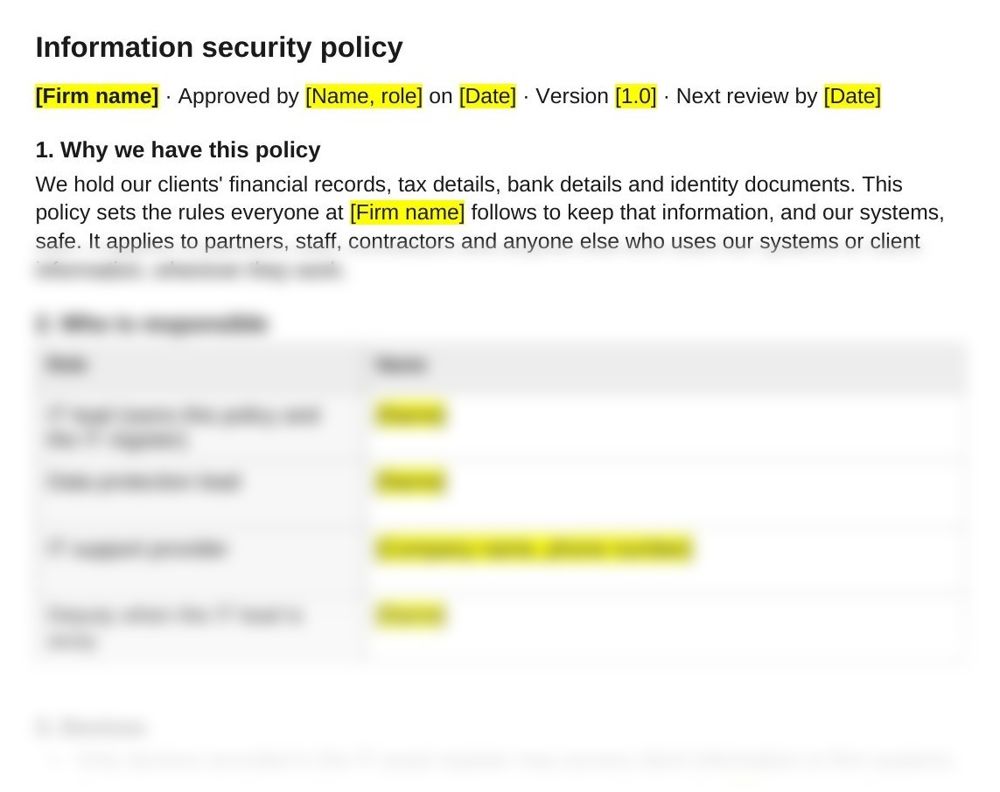
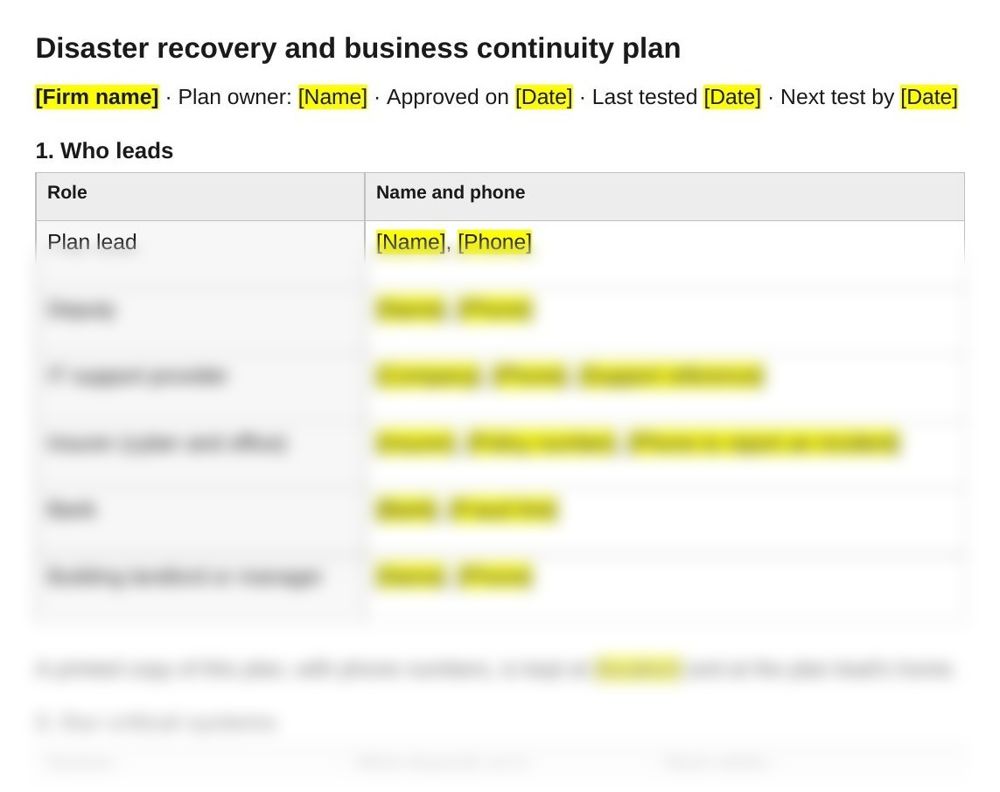
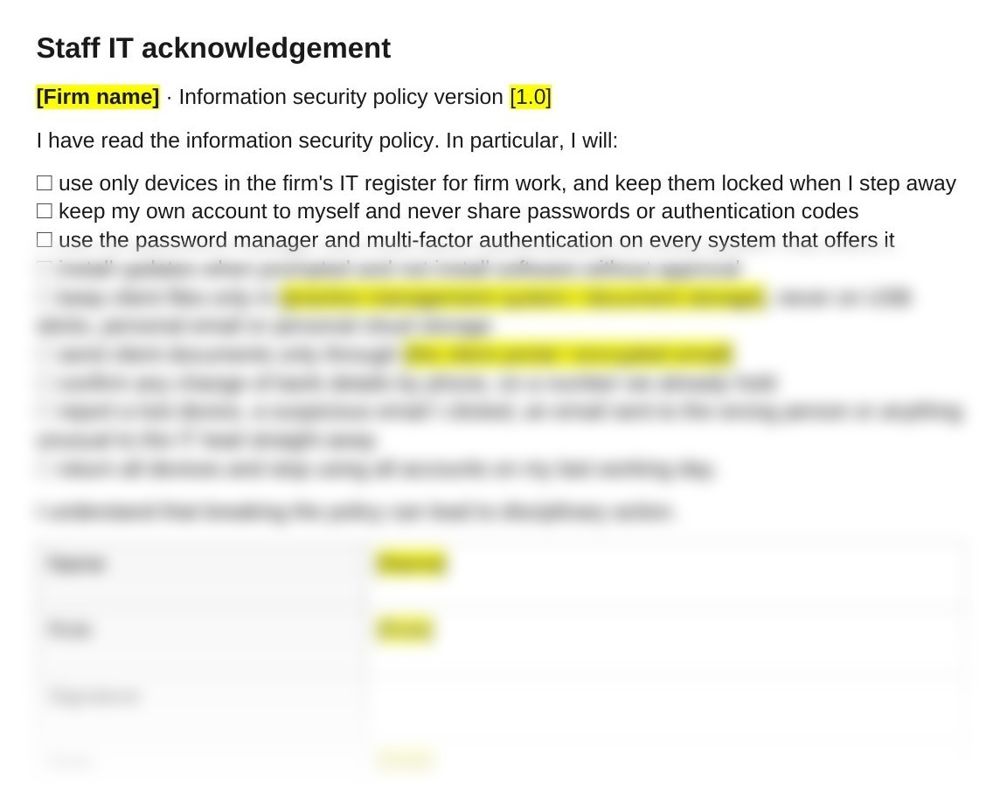
First page of each document. 5 files, Word and Excel.
What IT security involvesDocument in the pack
Written rules for devices, accounts and client data
✓Information security policyDevices, updates, passwords, email, client files and backups
Critical updates within 14 daysCyber Essentials v3.3
✓Policy and IT registerFlags devices not updated and software past its support date
Multi-factor authentication on cloud services where availableCyber Essentials v3.3
✓Policy and IT registerFlags cloud accounts where it is available but off
Separate administrator accounts and leavers removedCyber Essentials v3.3
✓IT registerFlags leavers still with access and accounts due for review
Reporting personal data breaches within 72 hoursUK GDPR art. 33
✓Policy and disaster recovery planWho decides and how the Information Commission is told
A plan for ransomware, lost devices and office closure
✓Disaster recovery and business continuity planFirst hour, five scenarios, client deadlines and a test record
Who it's for
Small UK accountancy and bookkeeping practices, with or without Cyber Essentials certification.
Last checked
Checked against the Cyber Essentials Requirements for IT Infrastructure v3.3 and UK GDPR breach reporting rules in November 2026.