Data breach procedure template for accountancy practices
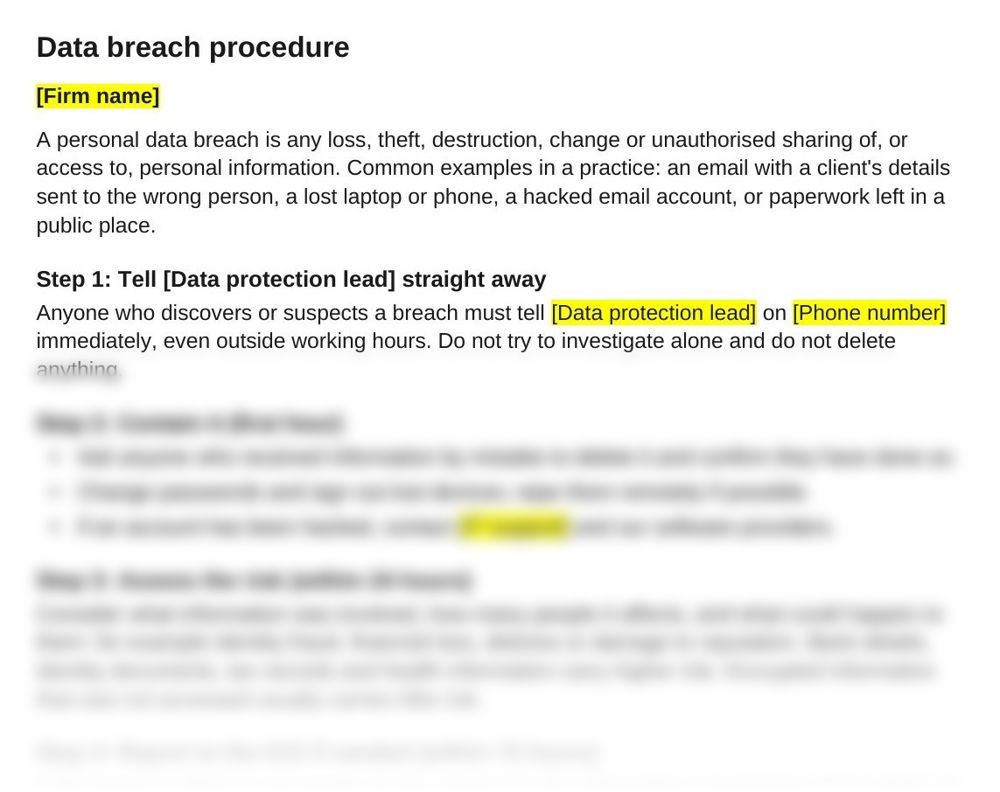
What your team does in the hours after an email goes to the wrong client, a laptop goes missing or an inbox is hacked. This data breach procedure template sets out seven steps on two pages, from the first phone call to the ICO report and the lessons learned.
UK practicesGet this pack and 100 more for $129
What the procedure looks like
When you need it
Every firm that handles personal information needs a plan before something goes wrong, because the 72-hour clock for reporting to the ICO starts when you become aware of the breach, not when you have finished looking into it.
- A client's tax return or payslips are emailed to the wrong person
- A laptop, phone or memory stick with client files is lost or stolen
- Someone gets into a staff email account or your practice software
- Paper files are left in a public place or put in the general waste
- A supplier tells you it has had a breach that affects your clients' data
How to use the data breach procedure template
- Fill in the names and numbers. Your data protection lead, their phone number, your IT support and, if you have one, your cyber insurer.
- Set the review period. Choose how soon after a breach the review in step 7 takes place.
- Give it to every member of staff. Include it in induction and keep a copy where people can find it out of hours.
- Use it with the breach log. The data protection logs in the same pack work out the 72-hour deadline from the time you became aware.
- Practise once a year. Walk through a misdirected email or a lost laptop with the team and check the contact details still work.
Questions
What is a personal data breach?
A breach of security that leads to the accidental or unlawful destruction, loss, change or unauthorised sharing of, or access to, personal information. It covers mistakes as well as attacks, so an email sent to the wrong client counts.
Do all data breaches have to be reported to the ICO?
No. You must report a breach unless it is unlikely to put people's rights and freedoms at risk. You must still record every breach, including the ones you don't report.
How long do you have to report a data breach?
Without undue delay and, where you can, within 72 hours of becoming aware of it. If you report later, you must give the reasons for the delay. If you don't have all the details yet, you can send the information in stages.
What must a breach report include?
What happened, roughly how many people and records are affected, a contact name, the likely consequences and what you have done or plan to do about it.
When do you have to tell the people affected?
When the breach is likely to put them at high risk. Tell them without undue delay, in plain language. You don't have to if the data was protected, for example by encryption, if later action means the high risk is no longer likely, or if telling each person would take disproportionate effort, in which case a public notice is used instead.
Also in the UK GDPR pack for practices
Who it's for
Accountancy practices that want their staff to know exactly what to do in the first 72 hours after a breach.
Last checked
Checked against Articles 33 and 34 of the UK GDPR on legislation.gov.uk in November 2026.