Data breach log template for accountancy practices
Record every personal data breach in one place, from a misdirected email to a stolen laptop, with the ICO deadline worked out from the moment you found out. This data breach log template is one Excel workbook, with logs for subject access requests and complaints alongside.
UK practicesGet this pack and 100 more for $129
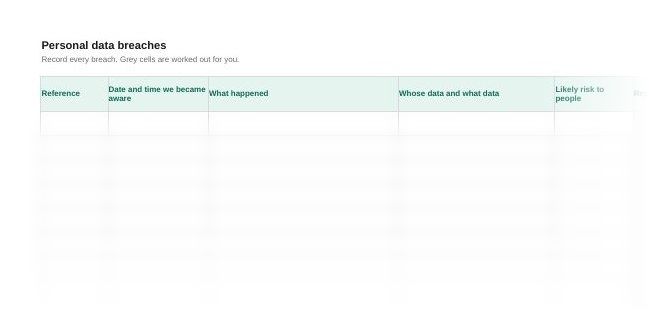
What the log looks like
When you need it
The UK GDPR requires you to keep a record of every personal data breach, with the facts, its effects and the action you took, whether or not you report it to the ICO. Add a row as soon as you know about a breach, for example:
- An email or letter goes to the wrong client
- A laptop, phone or box of papers is lost or stolen
- A staff email account is hacked
- Someone opens client records they had no reason to see
- A supplier tells you about a breach on their system that affects your data
How to use the data breach log template
- Start a row straight away. Enter the date and time you became aware. The grey Report to ICO by cell fills in.
- Describe the breach. What happened, whose data and what type of data.
- Judge the risk. Pick Unlikely, Risk or High risk. Red cells show what still needs doing.
- Record your decisions. Whether you reported it, your ICO reference, and whether you told the people affected.
- Close it. Write down the action you took and the date the matter closed.
- Keep it private. Store the workbook where only the people who handle breaches can open it.
Questions
What is a data breach log?
A record of every personal data breach your firm has had, with the facts, the effects and the action taken. Article 33(5) of the UK GDPR requires it, and the record must let the Information Commission check that you have complied.
Do you have to log breaches you don't report to the ICO?
Yes. The duty to record covers every breach. A breach that is unlikely to put anyone at risk does not have to be reported, but it still goes in the log, and the log shows the reason you didn't report it.
What should a data breach log include?
At least the facts of the breach, its effects and the action you took. This log also records when you became aware, whose data was involved, the risk to people, the ICO deadline, whether you reported it, whether you told the people affected and when the matter closed.
How long should you keep a data breach log?
The retention schedule in the same pack keeps data protection breach, subject access and complaints logs for six years from the date the matter closed, as evidence of compliance.
What would an empty data breach log indicate?
Either your firm has had no breaches, or staff are not reporting them. Emails sent to the wrong client and lost phones count as breaches, so make sure everyone knows to report every one, however small.
Also in the UK GDPR pack for practices
Who it's for
Accountancy practices that want one record of every breach and the deadlines that go with it.
Last checked
Checked against Articles 33 and 34 of the UK GDPR on legislation.gov.uk in November 2026.