Incident response plan template for tax and accounting firms
Know who does what, who to call and who to tell if client data is stolen, exposed or locked by ransomware. This incident response plan template is one Word plan, built around the FTC Safeguards Rule and the IRS steps for tax professionals.
US firmsGet this pack and 45 more for $69
You save $546 on buying them one by one
Buy the US library · $69Want every pack, for every region? Global library, 101 packs, $129
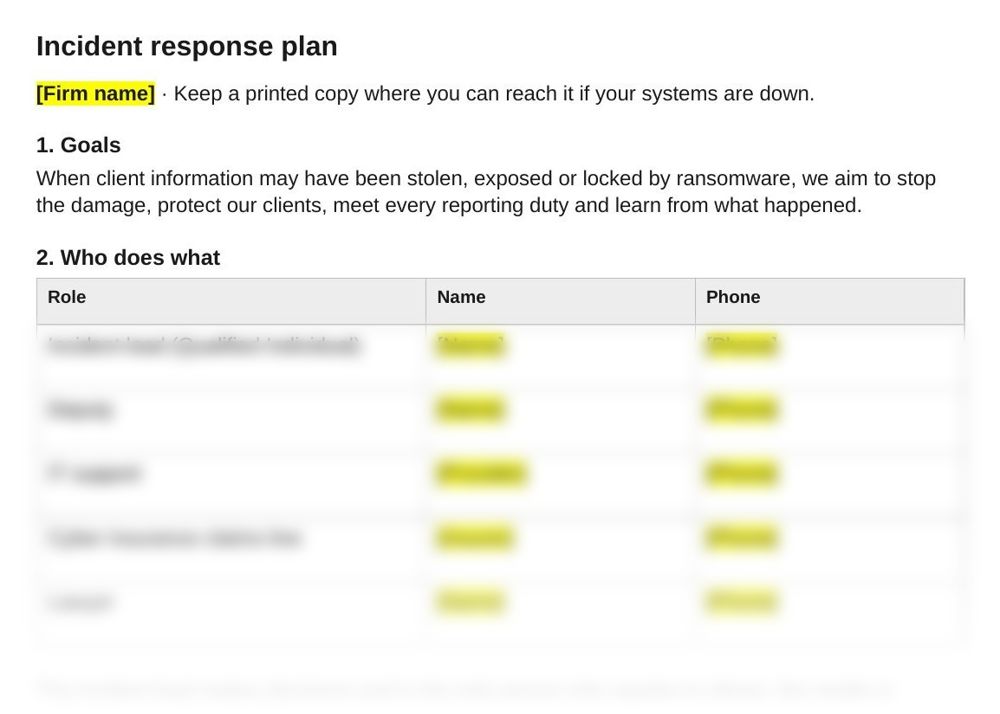
What the plan looks like
Who needs one
The FTC Safeguards Rule treats an accountant or other tax preparation service that completes income tax returns as a financial institution. Its information security program must include a written incident response plan, unless the firm holds customer information on fewer than 5,000 consumers.
- You prepare tax returns and hold information on 5,000 or more consumers
- You are writing or reviewing your written information security plan (WISP)
- Your cyber insurer asks how you would handle a breach
- A smaller firm that wants a clear plan ready before anything goes wrong
How to use the incident response plan template
- Fill in the contacts. Name your incident lead and deputy, and add phone numbers for IT support, your cyber insurer's claims line and your lawyer.
- Check your insurer's terms. Many policies require you to call them before hiring anyone else, so put that call in the first hour.
- Find your IRS Stakeholder Liaison now. Add the contact details before you need them, along with the state tax agencies where you prepare returns.
- Set the review period. Choose how soon after an incident you review what happened, and record the changes.
- Print a copy. Keep it where you can reach it if your systems are down, and walk your staff through it.
Questions
Do tax preparers need an incident response plan?
Yes, if the firm holds customer information on 5,000 or more consumers. The FTC Safeguards Rule counts tax preparation firms as financial institutions and requires a written incident response plan as part of their information security program. Firms below that number are exempt from this one requirement.
What should an incident response plan include?
The Safeguards Rule lists seven elements: the plan's goals, internal processes for responding, clear roles and decision-making authority, internal and external communications, fixing the weaknesses found, recording and reporting security events, and reviewing the plan after an event.
When do you have to notify the FTC of a data breach?
When unencrypted customer information about at least 500 consumers is acquired without their authorisation. You must notify the FTC as soon as possible and no later than 30 days after discovery, using its online form.
Who should a tax preparer contact after a data breach?
The IRS asks you to contact your local IRS Stakeholder Liaison first, so it can watch for fraudulent returns. Then the state tax agencies where you prepare returns, the FBI, your local police, and the state attorneys general where state law requires.
What should you do in the first hour of a breach?
Tell the incident lead, disconnect affected devices from the network without turning them off or deleting anything, change passwords from a clean device and call your IT support and cyber insurer.
Also in the WISP kit for tax and accounting firms
Who it's for
Small CPA, EA and tax preparer firms that need a written plan staff can follow on the day.
Last checked
Checked against the FTC Safeguards Rule and IRS guidance on data theft for tax professionals in November 2026.